
Firewall Security: 7 Best Practices for Protecting Modern Business Networks
A finance employee might connect through a home router. An inventory system might exchange data with a cloud platform. A contractor might sign in from a personal laptop.
None of this is unusual. Still, each connection creates another route into systems. Those systems may hold customer records, payment details, or operational data.
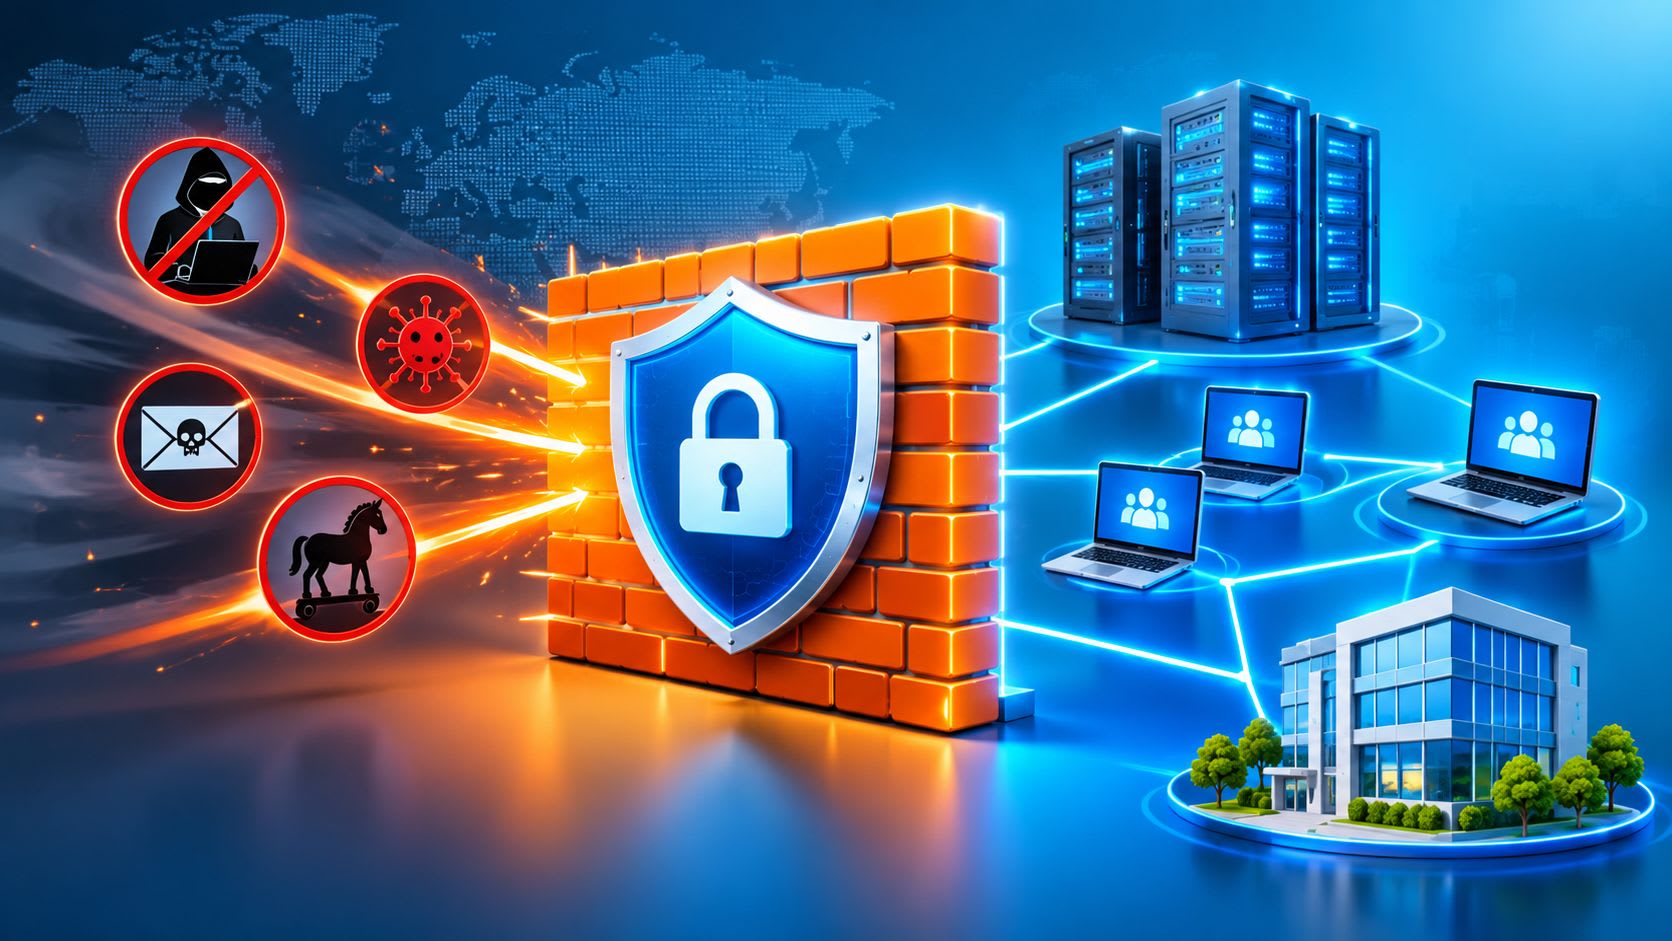
That’s why you can’t treat firewall security as a forgotten appliance installed at the office boundary. In fact, modern traffic moves among -
- Cloud workloads
- Remote devices
- Branch locations
- Software-as-a-Service (SaaS) applications
- Third-party systems.
A rule that made sense two years ago may now expose an abandoned server. It might also allow far more access than the business needs.
How to Ensure Effective Firewall Protection
Effective protection comes from disciplined policy work. In this case, you have to -
- Restrict traffic
- Document exceptions
- Inspect meaningful events
- Remove access when its business purpose disappears.
The hardware matters. However, everyday decisions determine whether the firewall remains a barrier or slowly becomes a collection of convenient holes.
1. Begin With a Default-Deny Policy
A default-allow approach permits traffic unless someone blocks it. That’s easy to operate at first, though the apparent convenience leaves security teams chasing new services, ports, and destinations after they’ve already appeared.
Default deny reverses the burden. Traffic is blocked unless an approved rule permits it. This gives firewall security for business networks a sound starting position. No need to rely on an ever-growing blacklist.
Each exception should identify:
- Source and destination addresses
- Required protocol and port
- Application or business service
- Rule owner
- Approval date and expiration date
- A ticket or change record explaining the need
Some legacy applications use broad port ranges or undocumented connections. Tightening those rules may break production, so monitor the traffic first, test the proposed restriction, and keep a rollback route ready.
2. Segment Systems by Business Risk
One flat network lets a compromised laptop reach various places. So, put the following into separate network zones:
- Employee devices
- Guest Wi-Fi
- Payment systems
- Production servers
- Backups
- Internet-facing services.
No need to start segmentation with an expensive redesign. A mid-size company might first separate guest wireless traffic from internal resources. Then, it might isolate finance systems and backups.
Firewall rules permit only the connections those zones require.
| Zone | Typical permitted connections | Traffic to block |
| Guest Wi-Fi | Internet access and approved DNS | Internal servers and management interfaces |
| Employee network | Business applications and shared services | Backup repositories and production databases |
| Public application zone | Required application and update traffic | Direct access to sensitive internal systems |
| Backup network | Scheduled traffic from approved hosts | User devices and unrestricted internet access |
Segmentation adds administrative work. This is especially true when applications were built around unrestricted internal access. Still, that friction is useful when it reveals hidden dependencies early.
3. Remove Stale and Excessive Rules
Firewall policies accumulate debris. The following situations are common:
- Temporary vendor access survives after a project ends
- Old IP addresses remain trusted
- Emergency rules lose their promised expiration dates.
So, review the rule base at least quarterly. Do monthly checks of higher-risk environments. In this case, start with
- Disabled rules
- Rules showing no hits during a meaningful observation window
- Duplicate entries
- Broad “any-to-any” permissions
- Access tied to former employees or suppliers.
Don’t delete a zero-hit rule blindly. A disaster recovery connection may stay quiet for months. Still, it matters during an outage. Confirm its owner and purpose. Then, either retain it with a review date or remove it through the normal change process.
4. Control Outbound Traffic Too
Many businesses scrutinize incoming connections. But they allow almost anything to leave. That weakens containment. Malware, unauthorized remote tools, and compromised accounts may communicate outward after getting inside.
Therefore, restrict outbound traffic by -
- Destination
- Application
- Protocol
- User group (where the firewall supports it).
In fact, servers rarely need the same browsing access as employee workstations. For instance, a database server may require approved update repositories and internal services. It does not need open access to every internet destination.
Should You Decrypt All Encrypted Traffic for Inspection?
Decryption can do the following:
- Expose sensitive information
- Increase processing costs
- Create privacy or regulatory concerns.
A risk-based policy works better. Just inspect relevant business traffic. Carefully exempt defined categories such as health portals or personal banking.
5. Protect Administrative Access
An attacker who gains firewall administrator credentials can change the rules. They also don’t get detected. Management interfaces therefore need stronger restrictions than ordinary business applications.
So, require the following:
- Multifactor authentication (MFA)
- Named administrator accounts
- Role-based privileges.
Permit management connections only from designated devices or a protected administration network. Also, disable internet-facing management panels. Ensure this unless a documented operational need makes them unavoidable.
Make sure to log the following:
- Successful sign-ins
- Failed attempts
- Configuration exports
- Policy changes
- Account modifications.
Shared administrator accounts muddy responsibility. Sometimes, several technicians use the same login. Then, an incident review may show what changed but not who changed it.
6. Send Logs Somewhere People Will Check
Forward logs to a centralized system. This way, events remain available if the firewall fails, is replaced, or gets compromised.
Then, prioritize alerts for denied connections to -
- Sensitive zones
- Repeated authentication failures
- Policy changes outside approved windows
- Unusual outbound destinations
- Sudden traffic spikes.
Logging every permitted packet may create noise and storage expense. It does not give the team a clearer picture.
Tune alerts against normal business behavior. Retention periods should also reflect investigation needs. They must also cover contractual or regulatory obligations affecting the organization.
7. Test Changes and Practice Recovery
Every meaningful firewall change needs -
- Peer review
- A test plan
- Defined success criteria
- A rollback procedure.
Back up configurations after approved changes. Then, store copies away from the device. Test restoration rather than assuming the backup works.
We’ve all seen configuration archives collected faithfully for years. But during an outage, no one remembers the encryption password.
Periodic validation should include -
- External port scans
- Internal segmentation tests
- Rule-sampling reviews
- Confirmation that alerts reach the responsible person.
Vulnerability scanners can reveal exposed services. But they won’t decide whether a permitted connection still has a legitimate business owner.
Strong Firewall Security Depends on Policy Discipline
Firewalls matter even where identity controls, endpoint detection, and cloud-native protections carry part of the load. But their job has changed.
They no longer guard one obvious perimeter. Now, they control traffic across smaller boundaries that follow applications, users, workloads, and data.
Good firewall security shows up in the unglamorous work:
- Narrow rules
- Named owners
- Tested recovery files
- Useful logs
- Access that actually expires.
Those habits reduce exposure. For a business owner, that means fewer unknown pathways into critical systems. So, you get a clearer account of what the network permits when something goes wrong.
Want to publish a guest post on aamax.co?
Place an order for a guest post or link insertion today.
Place an Order